[HIGH] CVE-2026-84998 — The NextScripts: Social Networks Auto-Poster plugin for WordPress is vulnerable to Stored Cross-Site Scripting via 'comment_author' and 'com
ThreatFilter threatfilter.dev
This is what was read here when it was published. threatfilter.dev no longer carries it in what it publishes now.
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.(vendor/severity tags below are heuristic) The NextScripts: Social Networks Auto-Poster plugin for WordPress is vulnerable to Stored Cross-Site Scripting via 'comment_author' and 'comment_agent' Comment Fields in all versions up to, and including, 4.4.8 due to insufficient input sanitization and output escaping. This makes it possible for unauthenticated…
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
 PM hails restored ties between China and Australia
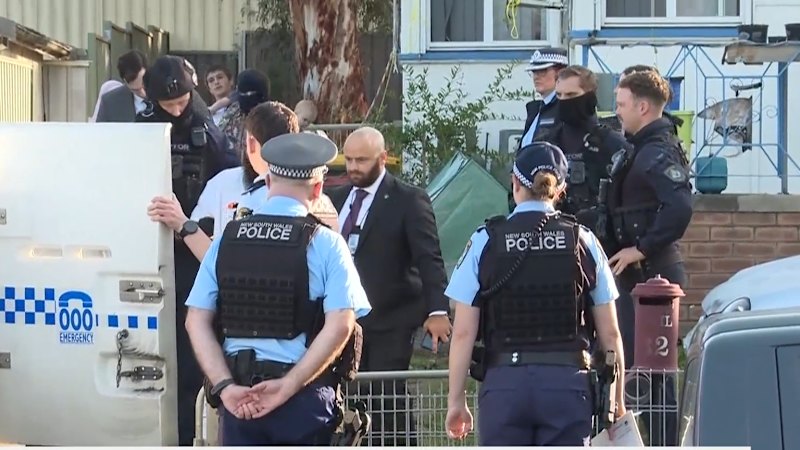 Counter-terrorism raids take place across Sydney
 Sweeping counter-terror arrests across Sydney
 Yesterday’s comments of note