CVE-2026-107942 — Improper Content Security Policy (CSP) nonce implementation in HCL BigFix MCM allows a remote attacker to reduce the effectiveness of the Co
ThreatFilter threatfilter.dev
Aurekai listening
Listen to this summary
Original instrumental score; voice stays in front.
Ready to listen
This reads the text available on this page using your browser's voice. It is not a publisher-recorded narration; voice processing depends on your browser.(vendor/severity tags below are heuristic) Improper Content Security Policy (CSP) nonce implementation in HCL BigFix MCM allows a remote attacker to reduce the effectiveness of the Content Security Policy protection mechanism via an orphaned nonce value in the style-src directive of the CSP header without a corresponding nonce attribute on any or element.
More ways to use this
Open on another device

Scan to open this page. Your saved notes and account access are not included.
 Identity context is essential for exposure management: Tenable One adds ways to bring in identity security data
 Java4Shell (CVE-2026-114938): Frequently asked questions about OpenJDK remote code execution vulnerability
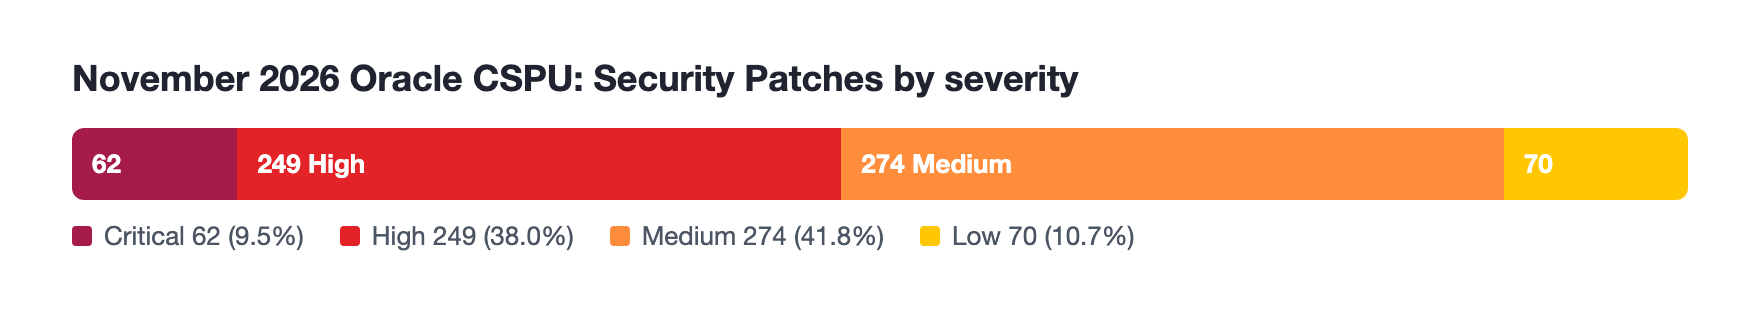 Oracle November 2026 Critical Security Patch Update Addresses 640 CVEs (CVE-2026-114938)